05Infrastructure lab
Virtualised infrastructure & network security
A Proxmox VE environment hosting monitoring tools and isolated test labs — segmented, firewalled and reachable only through encrypted tunnels.
- PlatformProxmox VE
- IsolationVLAN · SDN · firewall
- AccessVPN · bastion
| Role | Architecture, network segmentation, access control and automation |
|---|---|
| Context | Infrastructure lab |
| Stack |
- 01Remote userguest or admin
- 02VPN tunnelWireGuard overlay
- 03Bastionidentity & access
- 04Proxmox SDNVLANs · firewall
- 05VMsmonitoring · test labs
Platform
A Proxmox VE environment hosts the monitoring stack and isolated test environments, so experiments never touch production services.
Segmentation
- VLAN segmentation and Proxmox SDN zones.
- Firewall rules and strict inter-VM access policies.
Remote access
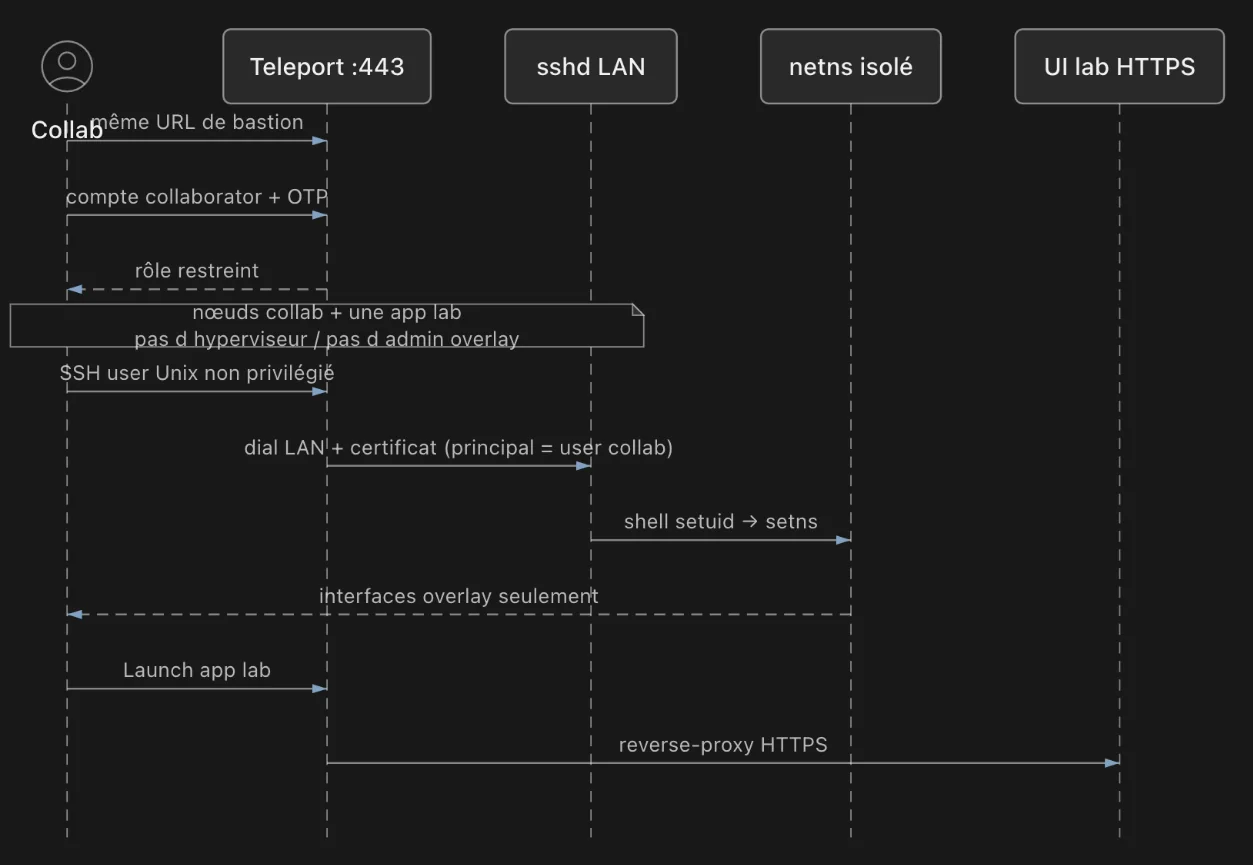
Encrypted access through VPN tunnels. An outside collaborator can be given access without ever seeing the internal network or the admin tools: a bastion handles identity and access for SSH and web apps, while a separate WireGuard overlay carries the traffic. Access control and network flows are two independent layers — either one blocks on its own.
Automation
Provisioning is scripted in Bash, so environments can be rebuilt the same way every time.
Zero Trust access, two planes
The need: give an outside collaborator access to the Proxmox environment without any visibility of the internal network or the admin tools — while keeping full admin access and without rebuilding what already ran.
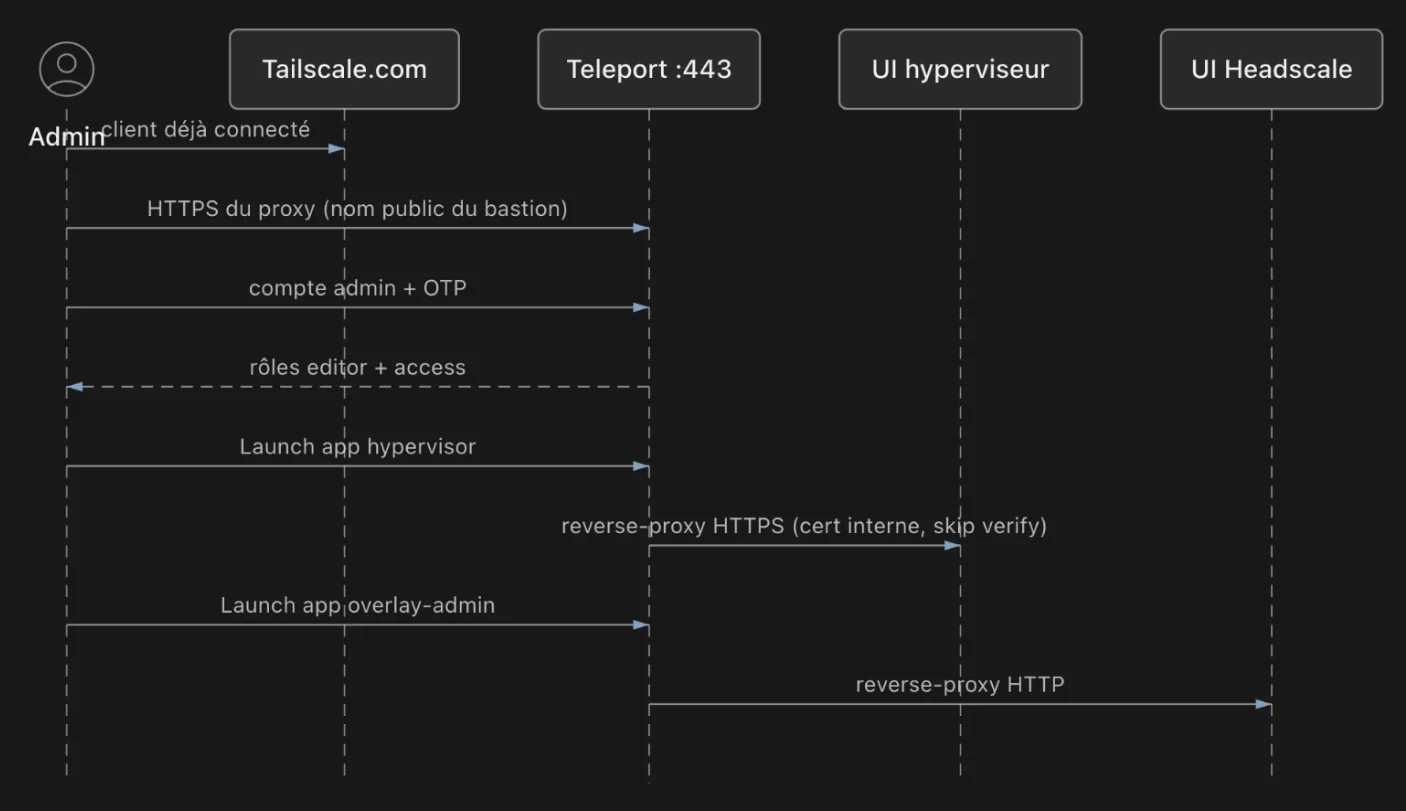
Teleport acts as the identity bastion (authentication, SSH and web application access) and Headscale provides a private overlay that stays invisible to the collaborator, who connects only through Teleport and installs no network client. My own admin access over Tailscale is unchanged.
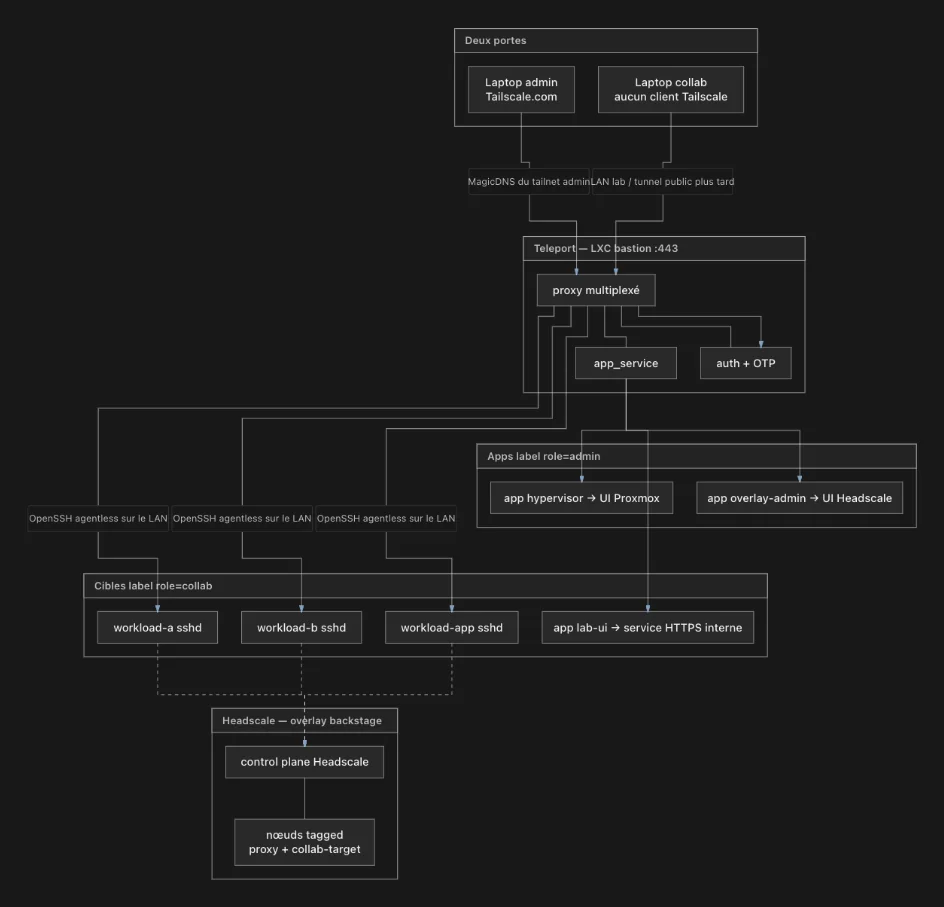
Key technical points
- Two overlay networks coexist on the same machine without interfering, thanks to a dedicated configuration that avoids any conflict.
- Strict isolation: the collaborator account has no route to the local network at all — only to the encrypted WireGuard overlay.
- Agentless SSH access, compatible with lightweight systems such as Alpine Linux.
- Two independent layers: application access control (Teleport RBAC) and network flow control (Headscale) — each can block access even if the other is misconfigured.
- Segmentation reinforced with Proxmox SDN.
Result
The collaborator reaches only what has been explicitly granted — specific web applications and SSH targets — with no view of the host or the admin network, and no impact on my own access.
Applied at work
The same practices are used day to day at MESEA on the supervision infrastructure of the high-speed line: Proxmox VE clusters (VMs, LXC containers, backup strategies), IP addressing, VPN and VLAN segmentation, OT / IT gateways, and Python and Bash scripts for deployment and supervision.